HIPAA-Compliant Meeting Notes for Healthcare Professionals
HIPAA prohibits the disclosure of Protected Health Information (PHI) without patient consent. Healthcare meetings — clinical discussions, case reviews, telemedicine calls — often contain PHI that standard AI note-taking tools aren't equipped to handle safely. HushSlate's local-first architecture changes that.
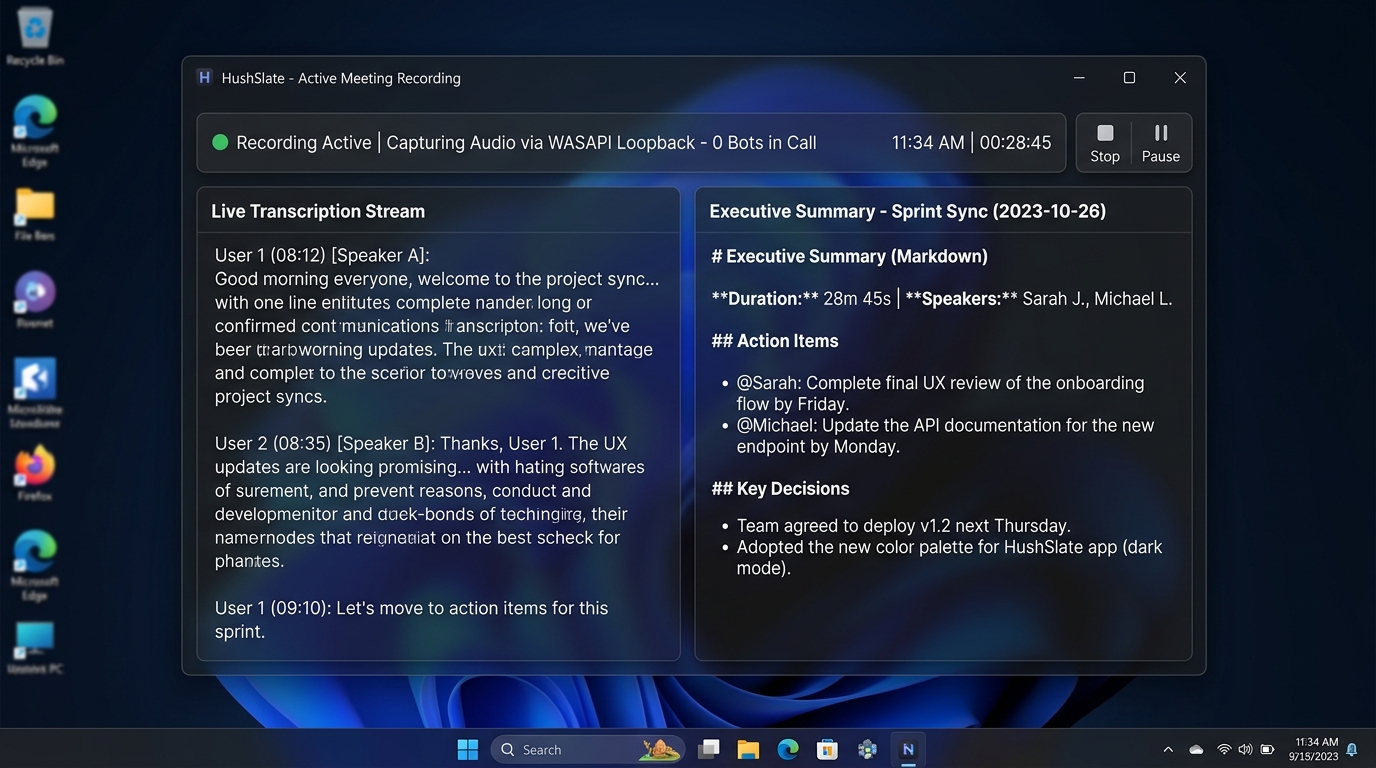
Core Architecture & Capabilities
HIPAA prohibits the disclosure of Protected Health Information (PHI) without patient consent. Healthcare meetings — clinical discussions, case reviews, telemedicine calls — often contain PHI that standard AI note-taking tools aren't equipped to handle safely. HushSlate's local-first architecture changes that.
Frequently Asked Questions
Is HushSlate HIPAA compliant?
HushSlate's architecture supports HIPAA compliance for healthcare organizations. Enterprise accounts include BAA execution for covered entities.
Can I record telemedicine calls with HushSlate under HIPAA?
With proper patient consent and a signed BAA with HushSlate, yes. Always consult your organization's compliance officer.
Does HushSlate offer Business Associate Agreements?
Yes — HushSlate Enterprise includes BAA execution for covered entities and business associates under HIPAA.
How does local recording help with HIPAA compliance?
Local recording keeps PHI on your device rather than uploading it to third-party servers during the session, reducing breach risk.
What should healthcare teams tell patients before recording?
Obtain explicit informed consent, explain the purpose of recording, confirm PHI will be protected, and document consent before the session begins.